Key Takeaways
- Evaluate AI and API capability on what they let you control, not on whether the vendor lists them
- The decisive AI question is where processing happens, inside the room or on an external service
- In-room AI inherits the room’s permissions and audit trail. Exported data does not
- An API matters when the data room has to fit an existing stack rather than sit beside it
- Ask about authentication method, not just whether an API exists
- Integration depth varies widely, and a listed integration is not the same as a supported one
- Documentation quality predicts implementation cost better than any feature list
Table of Contents
ToggleEvaluate a virtual data room on AI and API by asking three things: where AI processing happens and whether it stays inside the room’s permission model, what the API actually lets you automate beyond file upload, and how authentication and documentation are handled. Feature lists answer none of these.
Most vendor comparisons on these two topics reduce to checkboxes. Does it have AI. Does it have an API. Both questions can be answered yes by products that behave very differently once a deal is running.
The sections below cover what AI does in a data room, the governance question underneath it, what an API enables, and a checklist for putting both to a vendor.
What AI Actually Does in a Virtual Data Room
AI in this category is mostly pattern work over document sets, and it is useful in proportion to how large and unstructured those sets are.
- Document categorization. Sorting an unstructured upload into a diligence folder structure by recognizing document type. Saves the most time on carve-outs and on sellers who arrive with a shared drive rather than an organized set
- Redaction assistance. Flagging candidate passages containing personal data, pricing or named parties across thousands of pages. The flagging is automated; the decision should not be
- Q&A support. Suggesting which document answers an incoming question, and which previous answer covered the same ground
- Document comparison. Identifying differences across contract versions or between a template and an executed copy
- Translation. Useful on cross-border deals where local contracts are not in the review team’s language
Optical character recognition sits underneath several of these and is often marketed as AI. It makes scanned documents searchable by content, which matters on any deal involving decades of filed paper.
What none of these do is judgment. An extraction is not an assessment, and a tool presenting one as the other creates risk rather than saving time.
In-Room AI or External AI: The Question That Matters
Here is the question that separates vendors, and it is rarely on a comparison table.
When AI processes your documents, where does the processing happen? Two architectures are in the market and they carry different exposure.
| AI inside the data room | AI on an external service | |
|---|---|---|
| Where documents go | They stay under the room’s permissions | Copies leave for a third-party model |
| Audit trail | Processing is recorded like any other access | Often invisible to the room’s log |
| Permission model | AI inherits it. A reviewer sees only what they could already see | May bypass it, depending on implementation |
| Who to ask about it | The data room vendor | The data room vendor and the model provider |
The practical test is a question worth putting in writing: does any document leave the environment for AI processing, and if so, to which provider, under what retention terms, and is that processing recorded in the audit trail.
This matters beyond principle. Unauthorized AI use is now a measurable data-loss route. Verizon’s 2026 Data Breach Investigations Report places shadow AI as the third most common non-malicious insider data-loss event, up fourfold year over year, with source code the leading data type submitted to unauthorized platforms.
A vendor whose AI exports data is solving one problem while creating the one your security team is currently trying to close.
What a Virtual Data Room API Enables
An API is a defined set of instructions letting one program communicate with another. In this context it means your systems can drive the data room directly rather than someone doing the work by hand. Stripe and Twilio are the familiar examples: rather than building payment processing or SMS from scratch, developers call an existing service.
For a data room, that turns manual administration into workflow.
- Automating upload and folder creation, so a new deal in your CRM provisions a structured room without anyone building it
- Setting access control privileges programmatically, so permission groups follow your own user directory
- Applying rights management and dynamic watermarks to documents at the point they are shared
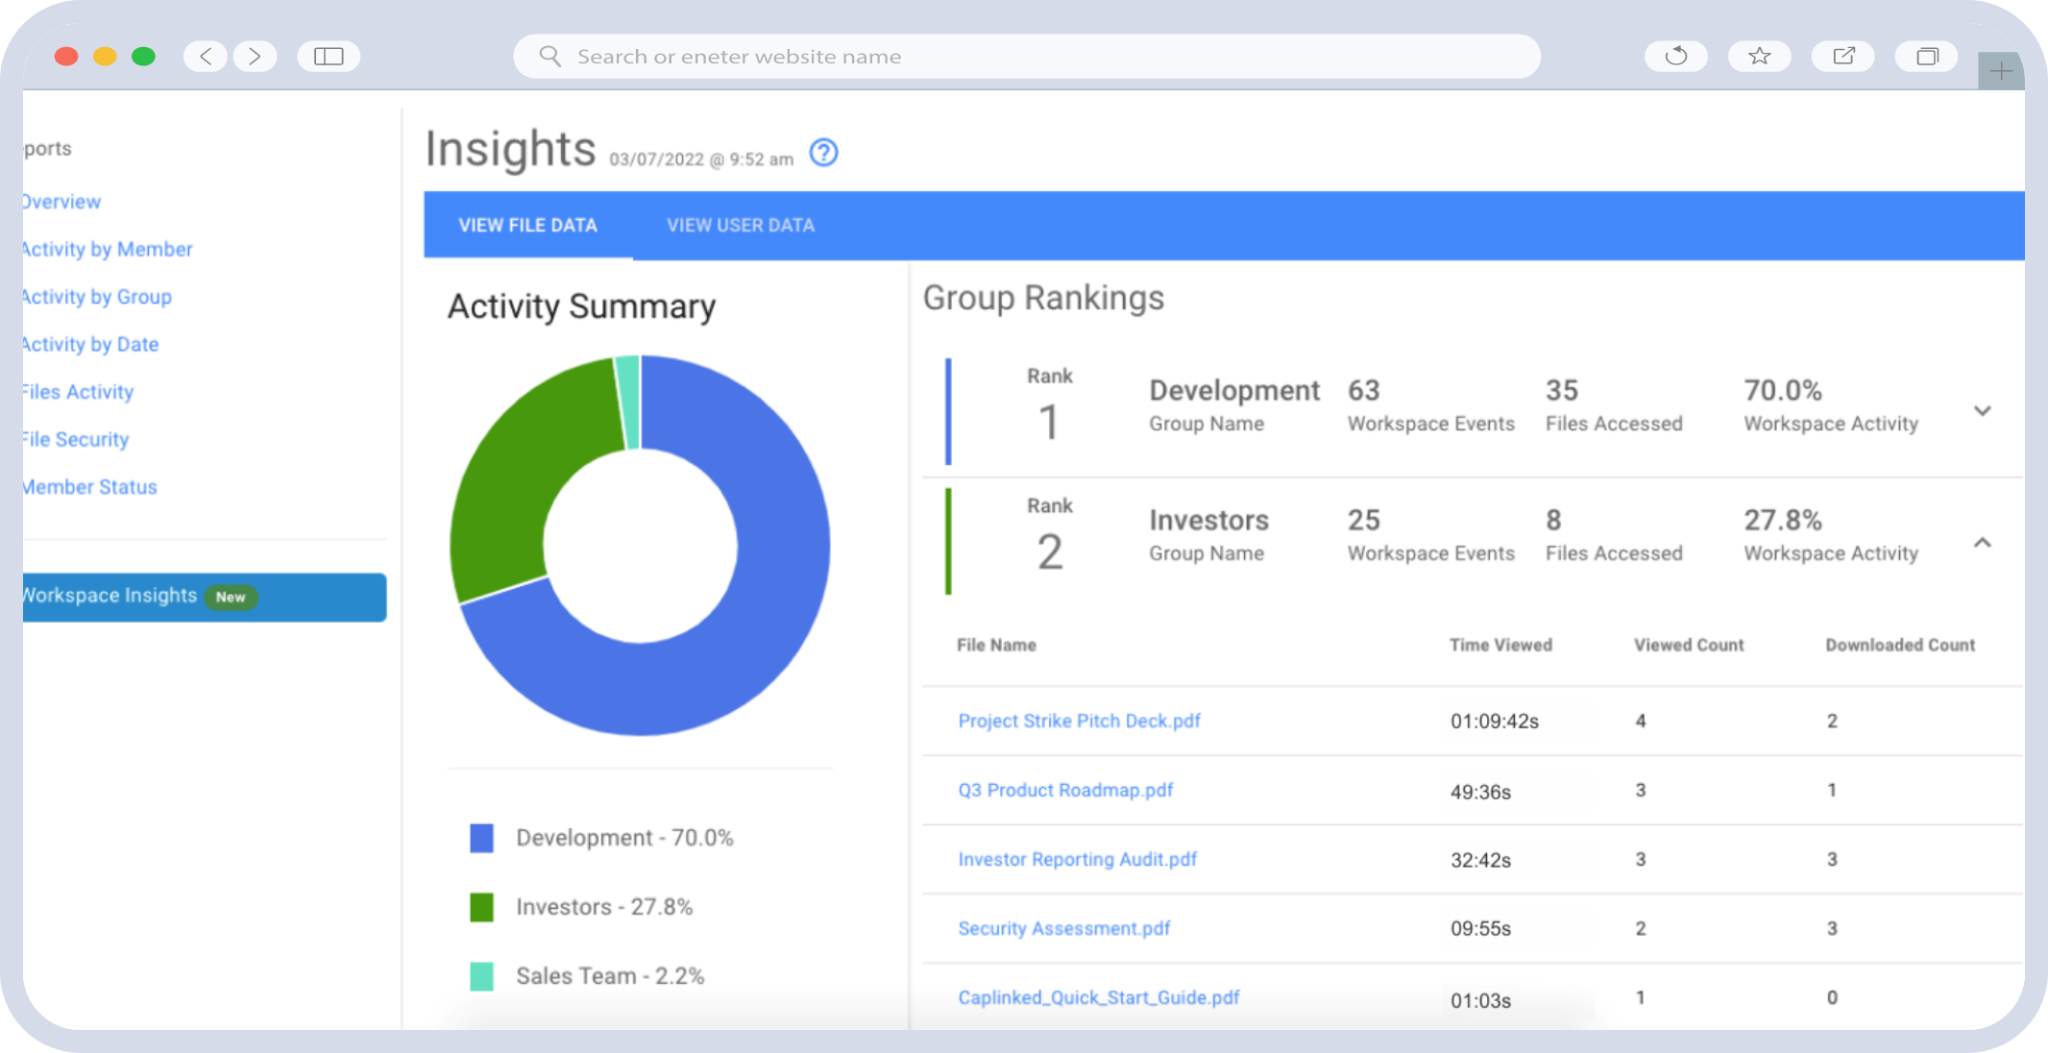
- Pulling activity data and audit trail reports into your own reporting rather than exporting by hand
- Protecting files that live in other applications, so the control follows the document rather than the location
The last one is the least understood and often the most valuable. It changes an API from a convenience for the deal team into a control layer across systems the company already runs.
Authentication and security
An API is an access route into confidential material, so the authentication model deserves as much scrutiny as the endpoints. CapLinked’s data protection API is built on RESTful principles and secured with HMAC public and private key authentication, TLS, and request signing, returning JSON with search, pagination and filtering.
Request signing is the detail worth understanding. It means each call carries a cryptographic signature derived from the request contents and your private key, so an intercepted call cannot be replayed or altered. An API secured only by a bearer token in a header does not offer that.
Integrations Worth Checking For
Integrations and an API solve overlapping problems. A prebuilt integration is faster when it covers your case exactly. An API matters when it does not.
| Category | What it connects | Why it matters |
|---|---|---|
| Identity and SSO | Your directory or identity provider | Removing someone from the directory removes their room access, without a separate step |
| CRM and deal tools | Pipeline and deal records | A new deal can provision a room rather than someone building one manually |
| Cloud storage | Existing document repositories | Avoids maintaining two copies of the same material during a live process |
| E-signature | Execution workflow | Keeps signature routing attached to the document set rather than running beside it |
One caution when comparing. A listed integration can mean a supported, maintained connector or a reference implementation somebody built once. Ask which, and ask who supports it when it breaks. CapLinked publishes its available integrations alongside the API for cases they do not cover.
How to Evaluate Vendors on AI and API
Nine questions, ordered by how much the answer should change your decision.
- Does any document leave the environment for AI processing, and to which provider?
- Is AI processing recorded in the audit trail alongside human access?
- Does AI respect the room’s permission model, or can it surface content a user could not otherwise open?
- What are the retention terms for anything sent to an external model?
- How does the API authenticate, and does it support request signing?
- Can the API set permissions and apply rights management, or is it upload and download only?
- Is there public documentation and a sandbox, or does evaluation require a sales conversation?
- Which integrations are supported and maintained, as opposed to listed?
- Is API access included, or gated behind an enterprise tier priced on request?
Question seven is the fastest signal. A vendor with public documentation and a free sandbox is confident in what it built. A vendor requiring a call before you can read the endpoint list is managing something.
| Practical Tip
Before shortlisting, read each vendor’s API documentation for fifteen minutes. Endpoint coverage, error handling and code examples tell you more about implementation cost than any feature comparison, and the exercise is free. |
How CapLinked Approaches API and Integrations
Taking the evaluation questions in order, here is what is documented.
On the API, CapLinked offers RESTful endpoints covering the operations that matter beyond file transfer: configuring access control privileges, applying enterprise rights management to Office and PDF files, creating dynamic watermarks carrying name, timestamp and IP address, generating user activity and audit trail reports, and running OCR search across stored files. Authentication uses HMAC public and private keys with TLS and request signing.
On documentation, the endpoint reference is public at the developer portal, and a free developer account includes an API key and a sandbox environment. You can assess the API before speaking to anyone.
On fitting an existing stack, the API can apply protection to files held in other applications, which is the enterprise information control case: control follows the document rather than depending on where it sits. Use cases span finance, CRM, audit, RFPs, project management, KYC, and investor and board portals.
On security posture, encryption is 256-bit AES at rest and TLS in transit, with independent SOC 2 assessment alongside ISO 27001, PCI SAQ-D and FISMA, set out in the security detail. On commercial terms, pricing is published rather than quote-gated.
Conclusion
Both halves of this evaluation reduce to the same question, which is how much control you keep. AI that runs inside the room keeps your permission model intact. An API that can set permissions and apply rights management extends that model into the systems around it. AI that exports documents and an API that only moves files both hand control somewhere else.
Ask the nine questions in writing and keep the answers. Vendors describe AI governance loosely in conversation and precisely in contracts, and the gap between the two is where the risk sits.
Then spend fifteen minutes in the documentation before you shortlist. It is the cheapest diligence available on this decision, and it is the step most buyers skip.
| Want to assess the API before talking to anyone? |
VDR AI and API FAQ
What does AI do in a virtual data room?
Categorizes uploaded documents, flags candidate passages for redaction, suggests which document answers a question, compares contract versions, and translates. It handles pattern work across large document sets rather than judgment.
Is AI in a data room secure?
It depends where processing happens. AI operating inside the room inherits its permissions and audit trail. AI that sends documents to an external service creates a third-party exposure your security team should assess.
What is a virtual data room API used for?
Automating room creation and uploads, setting access permissions programmatically, applying rights management and watermarks, pulling audit data into your own reporting, and protecting files held in other applications.
How should an API be secured?
Look for request signing alongside TLS, so each call carries a signature derived from its contents and your private key. An intercepted request then cannot be replayed or altered, which a bearer token alone does not prevent.
What integrations should a data room have?
Identity and single sign-on first, then CRM or deal tools, cloud storage and e-signature. Ask whether each is a maintained connector or a reference implementation, and who supports it when it breaks.
How do I compare VDR vendors on AI and API?
Ask where AI processing happens, whether it is audit-logged, how the API authenticates, whether it can set permissions, and whether documentation is public. Public docs and a sandbox are the strongest signal.
Does OCR count as AI?
It is often marketed that way. Optical character recognition makes scanned documents searchable by content, which is genuinely useful on paper-heavy deals, though it is a mature technology rather than a recent capability.