Key Takeaways
- ShareFile belongs to Progress Software and has done since October 2024, so the vendor documents sitting in your security file may name a company that no longer operates the platform.
- Both platforms hold the same mainstream certifications, which is why comparing Citrix ShareFile vs Dropbox on certifications will not tell you which one belongs on a live deal.
- The ShareFile vulnerabilities disclosed in February 2026 affected the on-premises Storage Zones Controller that customers host themselves, and not cloud-managed storage.
- Dropbox’s August 2026 incident came through a legacy Lenovo ID integration that let an attacker in without a password, which no certification review would have surfaced.
- Permissions decide who opens a document inside a platform, and they have no bearing on what happens to a PDF once a bidder saves it locally.
Table of Contents
ToggleShareFile and Dropbox hold the same mainstream certifications, so a badge comparison will not separate them. Each had a security event in 2026, and neither involved encryption: ShareFile’s affected an on-premises component customers host themselves, while Dropbox’s came through a legacy third-party login. What separates them for deal work is attack surface, identity, and control after download.
If you are weighing Citrix ShareFile vs Dropbox for a live transaction, most of what you will find compares storage limits, plan tiers, and e-signature features. That helps when you are choosing an everyday file tool, and it tells you very little about whether either platform belongs at the center of a competitive bid, which is the question this piece takes on. The pricing and feature side sits in a separate ShareFile and Dropbox feature comparison.
This is written for whoever has to defend the choice, whether that is the IT director running the security review, the general counsel who will be asked for an access log two years after closing, or the corp dev lead whose counterparty just sent over a security questionnaire. By the end you should know what actually differs between the two platforms, what to ask either vendor, and where general file sharing stops being appropriate for a transaction.
Is ShareFile Still a Citrix Product?
No. Citrix was taken private in 2022 and combined with TIBCO to form Cloud Software Group, and Progress Software completed its acquisition of ShareFile on October 31, 2024, paying $875 million for what its announcement describes as a business unit of Cloud Software Group. A great deal of the reference material in circulation predates both changes, which is why the Citrix name still appears in search results and in internal documentation.
The practical consequence sits in your vendor file. If your security review of ShareFile was completed while it was a Citrix product, the data processing agreement, subprocessor list, and SOC 2 report on record name a company that no longer operates the platform, and any BAA signed with a predecessor entity needs the same check. When a counterparty asks who processes your deal documents and under what terms, you have a current answer only if someone has requested the current documents. Ownership is worth confirming for any platform that has changed hands, which is one reason it belongs on the checklist alongside controls and certifications when you evaluate enterprise file sharing platforms.
Both Platforms Had a Security Event in 2026, and Neither Was an Encryption Failure
Any platform operating at this scale will have security incidents, and a disclosure is not a mark against a vendor, just as a quiet public record is no guarantee. Both 2026 events are worth reading closely for a different reason: in each case the encryption held and something else gave way, and the two failure points sit in very different places.
| Factor | ShareFile, February 2026 | Dropbox, August 2026 |
|---|---|---|
| What broke | CVE-2026-2699 and CVE-2026-2701, a pre-authentication chain in the Storage Zones Controller | A legacy Lenovo ID login integration |
| Root cause | Unauthenticated remote access to configuration pages on an internet-facing component | Dropbox accepted a third party’s assertion that a user controlled an email address, with no confirmation of its own |
| Who ran the affected part | The customer, on premises | Dropbox, through a federated identity partner |
| Scope | Customer-managed storage zones on v5 below 5.12.5. Progress states v6 versions are not impacted | Roughly 5,000 accounts, with content viewed and downloaded in some cases |
| Exposure window | Not publicly stated. Proof-of-concept code was published | August 4 to 21, 2026 |
| Vendor response | Patch to v5.12.5, or move to v6 | All Lenovo ID sessions expired, and a password is now required on that login path |
Table 1: What failed at each vendor in 2026, per vendor and government advisories
The ShareFile issue sat in a component customers host themselves
The February 2026 vulnerabilities allow, in Progress’s own words, an unauthenticated remote attacker to reach an on-premises storage zones controller’s configuration pages, which can lead to configuration changes and remote code execution. The MS-ISAC advisory published on April 2, 2026 notes that public proof-of-concept code was released, and neither CVE appears in CISA’s Known Exploited Vulnerabilities catalog as of its September 24, 2026 release, so there is no government confirmation of exploitation in the wild.
Scope matters here, and it cuts in ShareFile’s favor. Only organizations that chose to run their own storage zones were affected, usually for data residency or regulatory reasons, and cloud-managed ShareFile storage was never in scope. What the disclosure does tell you is where to look during a review, because CISA’s catalog holds two earlier entries for the same component: CVE-2021-22941, added in March 2022 and flagged for known ransomware campaign use, and CVE-2023-24489, added in August 2023 and described as allowing an unauthenticated attacker to remotely compromise customer-managed ShareFile storage zones controllers. Three remote-compromise issues in one self-hosted, internet-facing component over four years is reasonable grounds for asking whether you want that component anywhere in the path of deal documents.
The Dropbox issue arrived through a trusted third party
The Dropbox event had nothing to do with storage security. Between August 4 and 21, 2026, an attacker exploited a flaw in Lenovo’s email verification process to register a Lenovo ID using someone else’s address, then used a legacy integration to authenticate into the matching Dropbox account. According to reporting on the disclosure, Dropbox “trusted Lenovo’s assertion that the attacker controlled the email address without requiring confirmation through the existing Dropbox login method,” and the attacker viewed and downloaded content from some of the roughly 5,000 affected accounts. Lenovo said its own customers were not affected and that it worked with Dropbox to mitigate the risk.
A similar pattern shows up in Dropbox’s May 2024 Form 8-K, which disclosed unauthorized access to the Dropbox Sign environment, exposing emails and usernames for all users of that product and, for some, phone numbers, hashed passwords, API keys, OAuth tokens, and multi-factor authentication information. That filing stated there was no evidence the threat actor reached the production environments of other Dropbox products. Our look at Dropbox security incidents covers the earlier history, and a companion piece asks whether Dropbox is secure enough for business use.
What a deal team should take from this
Neither event argues for or against either brand, though both argue against evaluating a platform on its certification list. The Dropbox failure is the one worth studying, because an authentication path inherited from a partnership nobody has reviewed in years is now among the most common ways into a system. Verizon’s 2026 Data Breach Investigations Report found that 48% of breaches involved a third party in some capacity, a 60% increase year over year, while exploitation of vulnerabilities reached 31% of breaches and credential abuse fell to 13%. The same report found only 26% of known exploited vulnerabilities were fully remediated in 2025, down from 38%, which is the gap the ShareFile pattern above sits inside.
| Worth Knowing
Third parties featured in 48% of confirmed breaches in Verizon’s 2026 dataset, up from 30% a year earlier (Verizon 2026 Data Breach Investigations Report). When you review a file-sharing vendor, the integrations and identity providers it trusts belong inside the review. |
| Running a security review before a live process?
CapLinked publishes its full certification and control list, including the encryption standards, access controls, and audit capabilities your counterparty is likely to ask about. |
Where the Two Security Models Actually Differ
Set the incidents aside and the platforms still diverge once external parties are involved. G2’s data as of September 2026 puts ShareFile at 4.2 out of 5 across 1,542 reviews and Dropbox at 4.4 across 31,418, with ShareFile scoring 9.0 on security against Dropbox’s 8.8, and the two tie at 8.2 on change tracking and audit logs. That tie is the number worth pausing on, since audit depth is where a platform handling a competitive bid ought to pull away from a general collaboration tool.
The segment split says more than the ratings do. Dropbox’s reviewer base is 64.0% small business and 13.3% enterprise, while ShareFile’s is 40.1% small business and 26.3% enterprise, and the two products assume different things about who administers them day to day.
| Security consideration | Dropbox | ShareFile | What to verify |
|---|---|---|---|
| Primary design goal | File sync and team collaboration | Client-facing document exchange and portals | Whether controlled external disclosure is a core use case or an adaptation |
| Attack surface you own | Cloud only | Cloud, or customer-managed storage zones if you deploy them | Whether any component is yours to patch |
| Identity and federation | Several third-party login paths | Enterprise SSO and SAML on higher tiers | Which federated paths exist, and whether you can disable them |
| Permission granularity | Folder and file sharing controls | Folder, file, and role-based controls | Whether you can separate rival bidders cleanly |
| Audit record | Activity and change tracking | Activity and change tracking | Whether the full log exports, and how far back it retains |
| Post-download control | Not a core capability | Watermarking and information rights management on higher tiers | What happens to a file after a bidder saves it |
| Compliance gates | HIPAA eligibility with a BAA on business plans | HIPAA eligibility with a BAA on Premium and above | Whether your regime is covered on the tier you are buying |
Table 2: Security criteria that separate the two platforms in transaction work, as of September 2026
Two of those rows decide most deal situations. Customer-managed storage zones mean you have accepted responsibility for patching an internet-facing component with a documented history, and a counterparty’s security team may well ask who does that and how quickly. Post-download control is the second, and it is where both platforms and the wider category of general file-sharing tools run out of road.
What Happens After a Bidder Downloads the File?
Permissions govern access inside a platform, so once a reviewer downloads a document, permissions have done everything they can do. A large share of the exposure in a transaction starts at that moment.
Consider how a sell-side process ends for the bidders who do not win. Four parties may have had access to customer contracts, a cap table, and three years of financials, and by the end two have withdrawn at the indication-of-interest stage, one has dropped out after management meetings, and one has signed. Revoking platform access for the three who left takes a few minutes, while every file their teams downloaded still sits in local folders and email, outside any system you control and covered by a confidentiality agreement that operates as a promise instead of a control.
This is the point where a transaction platform and a general storage tool part company. Storage products are built to make sharing easy and durable, which is close to the opposite of what a controlled disclosure needs. CapLinked’s FileProtect digital rights management converts protected documents to PDF on download, applies watermarks carrying the viewer’s email address, IP address, time, and date, blocks printing and re-sharing of the downloaded copy, continues reporting activity after the file leaves the workspace, and permits revocation later, which renders downloaded copies unusable. Access can also be tied to workspace expiry, so protected downloads stop working when the room closes.
None of that means information can never escape, since someone can photograph a screen and no platform prevents it. What changes is that a leaked page carries an identity, and a withdrawn bidder’s copy can be switched off instead of negotiated back. Our rundown of virtual data room features deal teams should demand covers how this sits alongside permissions, watermarking, and activity tracking as one set of controls.
| Want to test post-download control on real documents?
Start a 14-day trial, protect one folder, download a file as a guest user, then revoke it and see what happens. |
The Security Questions Your Counterparty Will Ask
Buyer’s counsel and institutional security teams rarely ask which certifications a platform holds, because they are trying to establish whether anyone is actually operating it. Send these to either vendor before a process opens, and answer them about your own setup first.
| Question | Why it decides something |
|---|---|
| Which legal entity processes our data today, and can we see the current DPA? | Ownership changes leave the paperwork in your file out of date, as ShareFile’s two transitions show |
| What is the current subprocessor list? | Your counterparty’s questionnaire will ask, and a stale answer stalls the review |
| Is any component deployed on our own infrastructure? | If yes, patching responsibility is yours, and so is that component’s vulnerability history |
| Which third-party login paths can reach our data, and can we turn them off? | This is the exact failure mode behind the August 2026 Dropbox incident |
| How quickly will you notify us of a security incident, and is it in the contract? | Marketing pages do not commit to a timeline. Contracts do |
| Does the audit log export in full, and what is the retention period? | An access record you cannot export is not evidence you can hand to counsel |
| Can access to a downloaded document be revoked? | Determines whether a withdrawn bidder’s copy is a control or a conversation |
Table 3: Vendor security questions to resolve before a transaction opens
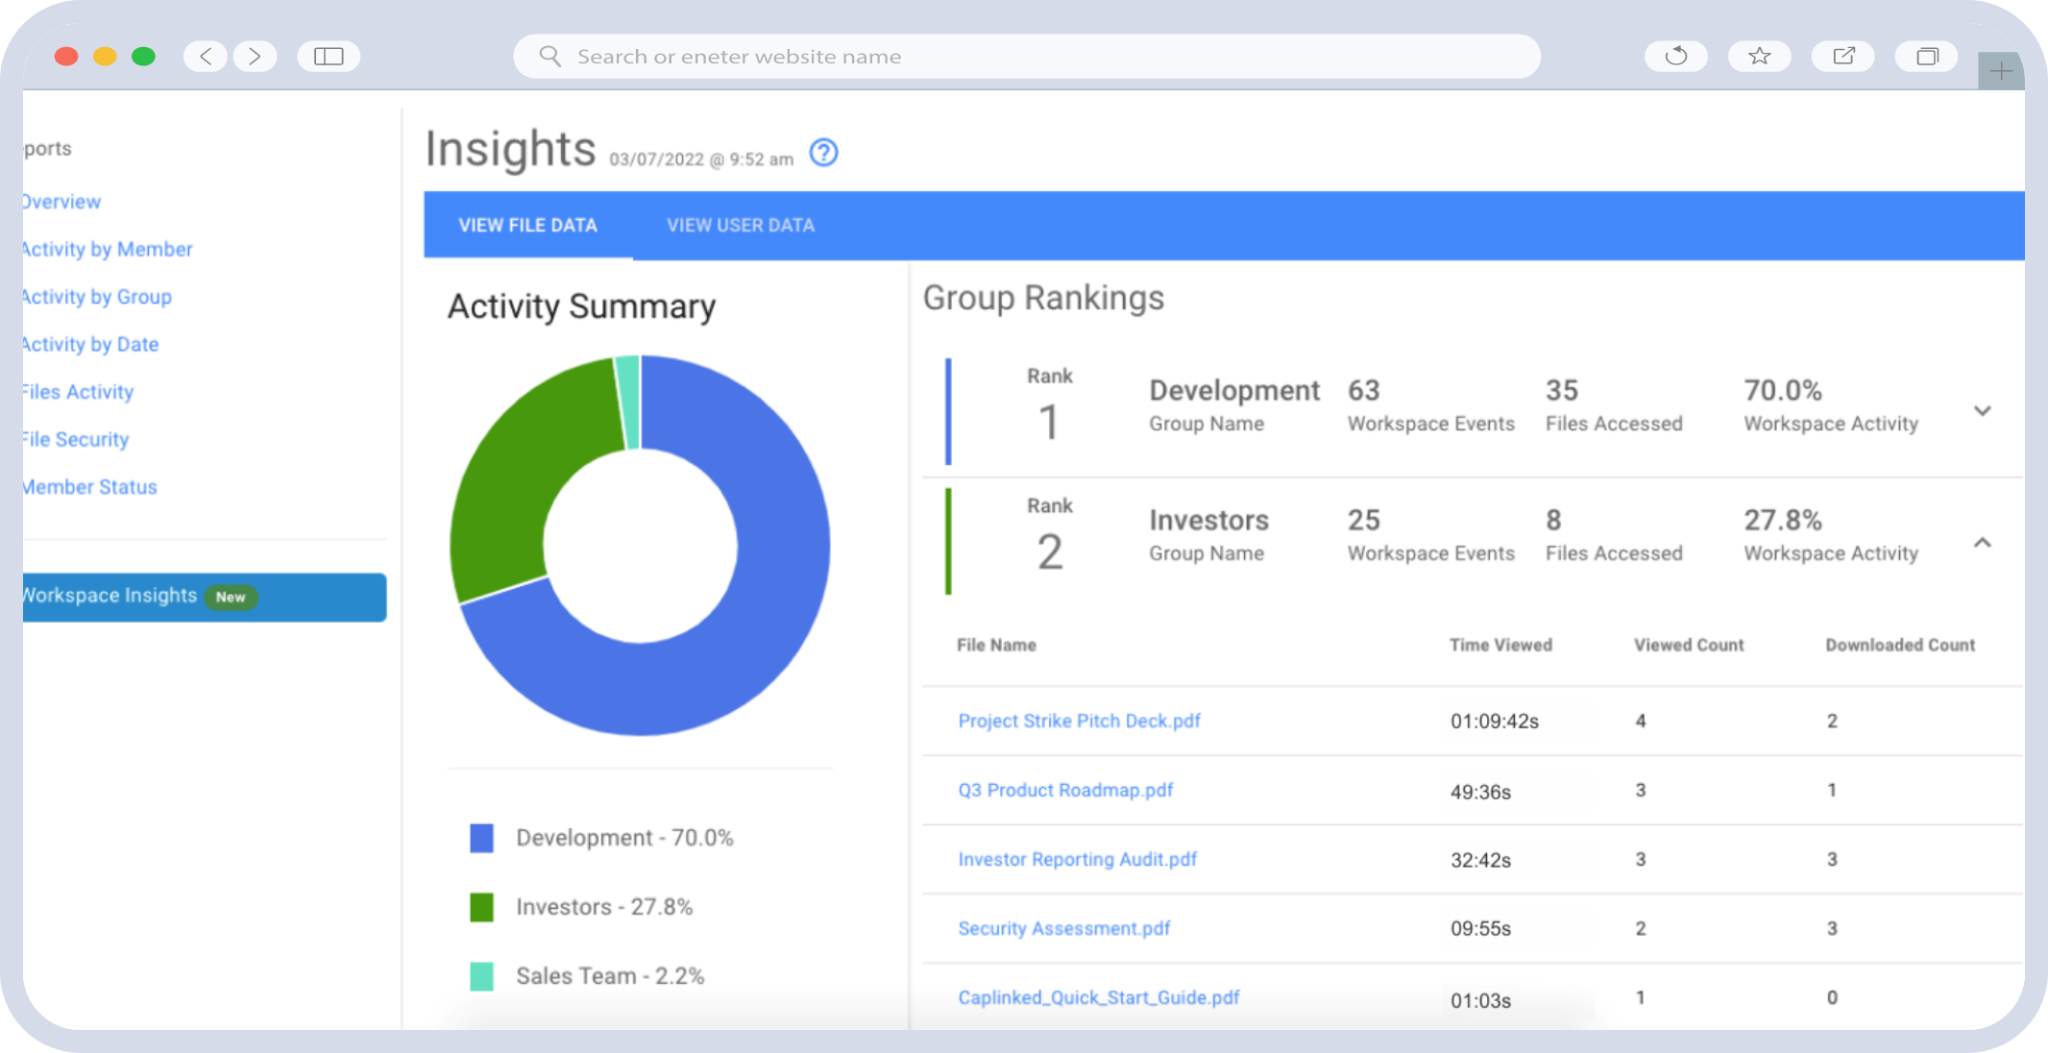
The last two carry the most weight for anyone who may end up in a dispute, since an audit trail earns its value years after closing, when a representations and warranties claim turns on who saw a disclosure schedule and when. CapLinked archives a complete history of document activity in each workspace and reports views, opens, and downloads at the user level, with exports available. Our guide to how data room access control works walks through how permission groups and audit records fit together, alongside a companion piece on data privacy practices for virtual data rooms.
When ShareFile or Dropbox Is Genuinely the Right Choice
Plenty of document workflows do not call for a data room at all. Dropbox is a capable everyday platform for internal collaboration, file synchronization, and sharing material that is confidential without being contested, so if your team lives in shared folders and your external sharing goes to known, stable counterparties, swapping it for a transaction platform solves a problem you do not have.
ShareFile suits recurring client-facing exchange. An accounting firm collecting tax documents, a law firm delivering closing binders, or a wealth manager sharing statements is doing repeat delivery to known clients, which is what a client portal was built for, and ShareFile also sells a dedicated virtual data room tier for transaction work.
The line falls where disclosure turns competitive and staged. Once several bidders who may be rivals are reviewing overlapping but deliberately different document sets, advisors are joining on each side, and access has to expand and contract as the process moves, you are administering a disclosure process instead of a folder. That distinction sits at the center of our piece on virtual data rooms versus file-sharing apps, and it is worth settling early, since companies notified US antitrust agencies of 2,006 reportable transactions in fiscal year 2025, with roughly 31.8% valued above $1 billion, according to the FTC and DOJ annual report published in July 2026.
Regulated Deals Narrow the Shortlist Before Features Matter
For readers in regulated sectors, everything above is secondary, because a missing standard removes a platform from consideration before anyone opens a feature grid. ShareFile and Dropbox both offer HIPAA eligibility with a business associate agreement, though the qualifying plan differs, so confirm which tier your quote covers instead of assuming the entry plan qualifies. Our explanation of what makes file sharing HIPAA compliant covers the BAA requirement and its limits, and financial services teams face a parallel set of obligations set out in our guide to FINRA-approved cloud storage requirements.
Defense and government work is stricter again. Contractors handling controlled unclassified information are assessed against Cybersecurity Maturity Model Certification requirements, and agency work brings FedRAMP obligations that most general collaboration tools were never positioned for, which is why CapLinked runs CMMC-oriented data room environments for that work. Cross-border deals add data residency as a further constraint, covered in our piece on cross-border M&A.
CapLinked publishes its own posture instead of holding it for a sales call. Data is encrypted using 256-bit AES at rest and SSL/TLS in transit, hosted on AWS infrastructure carrying SOC 2 and ISO 27001 certification, with the platform independently assessed against SOC 2 standards, HIPAA and HITECH requirements met including support for signing BAAs, PCI SAQ-D compliance, and FISMA requirements met through NIST SP 800-53 controls. Workspaces run in the browser with no plugins for guest users, which removes one class of client-side exposure and one common source of friction with a bidder’s counsel. The full control list sits on the CapLinked security page, and private equity teams running repeat processes may prefer to start with our comparison of data rooms for private equity.
Why Choose CapLinked As A Better Alternative to ShareFile & Citrix?
Put the certification lists away, because both platforms hold the mainstream ones and checking them would not have caught either 2026 incident. Four questions separate these products in practice: how much internet-facing infrastructure are you agreeing to run and patch, which identity paths can reach your documents, whether the audit log comes out in a form you could hand to counsel, and what you can still do about a document after a bidder has downloaded it.
Answer those and the decision usually makes itself. If your external sharing is routine delivery to known parties, your existing tool is probably adequate and the feature and pricing comparison will serve you better than this piece. If you are about to open a competitive process where rival bidders, their counsel, and their accountants all need different views of the same document set, and where you may need to prove who saw what long after closing, then you are buying disclosure control and not storage. CapLinked was built for that second case, with permission groups, identity-carrying watermarks, revocable downloads, and a full activity record included on the entry plan. Current plans and prices sit on the pricing page.
| Start Your Free Trial |
Frequently Asked Questions
Is ShareFile owned by Citrix?
No. Citrix became part of Cloud Software Group in 2022, and Progress Software completed its acquisition of ShareFile on October 31, 2024 for $875 million. Older reviews and documentation still refer to it as Citrix ShareFile.
Which is more secure, ShareFile or Dropbox?
Neither holds a decisive advantage on certifications, and both had a 2026 security event. ShareFile scores marginally higher on security in G2 reviews, while the two tie on audit logging. Which security model fits your deployment is the better question.
Was ShareFile affected by the 2026 vulnerabilities?
CVE-2026-2699 and CVE-2026-2701 affected customer-managed Storage Zones Controller deployments on v5 below version 5.12.5. Progress states v6 versions are not impacted. Organizations using ShareFile’s cloud-managed storage were not in scope.
Has Dropbox been breached recently?
Roughly 5,000 Dropbox accounts were accessed between August 4 and 21, 2026 through a legacy Lenovo ID integration that bypassed password verification. Dropbox expired all Lenovo ID sessions and now requires a password on that login path.
Can you use Dropbox for M&A due diligence?
It works for a simple bilateral deal with a small document set. Once several bidders need different access, advisors join each side, and you need an exportable access record plus control over downloaded files, a data room is the appropriate tool.
Does ShareFile or Dropbox let you revoke a downloaded document?
ShareFile offers watermarking and information rights management on higher tiers. Dropbox does not treat post-download control as a core capability. Confirm with either vendor which tier includes it and what the control does after a file leaves the platform.
What should you ask a file-sharing vendor before a deal?
Ask which legal entity processes your data, for the current subprocessor list, whether any component is yours to patch, which third-party login paths exist, the contractual incident notification window, and whether the audit log exports in full.